Industries · Government
Every security claim in the proposal has to match your SSP.
Federal, state and local RFPs, FedRAMP and NIST questionnaires and agency security reviews all ask for the same evidence. Tribble answers them from what your contracts, security and capture owners already approved, and sends only the new questions back to them.
- 3.1Describe your FedRAMP authorization status and the boundary it covers. SecurityApproved answer, reused
- 3.4Describe how you implement the NIST SP 800-53 access control family. SecurityApproved answer, reused
- 4.2Confirm compliance with the basic safeguarding clause, FAR 52.204-21. ContractsApproved answer, reused
- 5.1Provide a Section 508 VPAT for the proposed solution. ProductApproved answer, reused
- 6.2Provide three past performance references of similar size and scope. CaptureNew, sent to its owner
The documents agencies and primes send.
Grouped by who owns the answer. Every one draws on the same approved documentation.
| Document | What it asks for | Answer it with |
|---|---|---|
| Security and compliance | ||
| FedRAMP security questionnaires | Authorization status, boundary, control implementation and continuous monitoring | Security questionnaires → |
| NIST SP 800-53 and 800-171 questions | Control implementation statements, drawn from your SSP and policies | Security questionnaires → |
| State and local security reviews | StateRAMP, TX-RAMP and agency-specific questionnaires | Security questionnaires → |
| Contracts | ||
| FAR and DFARS clauses | Compliance statements, representations and flow-down requirements | Proposal automation → |
| Capture and proposal | ||
| Federal RFPs and task orders | Technical approach, management plan and past performance volumes | RFP automation → |
| State and local RFPs | Scope, qualifications, pricing forms and jurisdiction requirements | RFP automation → |
| Sources sought and RFIs | Capability statements and market research responses | RFP automation → |
| Product | ||
| Accessibility questions | Section 508 conformance and VPATs | RFP automation → |
Three kinds of buyer, three kinds of review.
Federal civilian agencies
Contracting officers score each volume against the solicitation, and security reviews the cloud authorization on its own track.
- They send
- RFPs, task orders, FedRAMP and NIST questionnaires
- They check first
- FedRAMP status, past performance, Section 508
Defense and the defense industrial base
DoD solicitations add DFARS clauses and CMMC requirements, and primes pass them down to every subcontractor.
- They send
- RFPs, DFARS and CMMC questions, supplier questionnaires
- They check first
- NIST SP 800-171, CMMC level, export control
State, local and education
Each jurisdiction runs its own procurement rules and its own security review.
- They send
- RFPs, StateRAMP and agency security questionnaires, pricing forms
- They check first
- Jurisdiction requirements, security posture, references
One question, start to finish.
What happens to a single question when a FedRAMP section lands.
The question
Describe your FedRAMP authorization status and impact level, and which components of the proposed solution fall inside the authorization boundary.
Example: agency security questionnaire, owned by your security lead
- 01
It comes in
The questionnaire arrives as the agency’s spreadsheet, a PDF attached to the solicitation or a portal export. Tribble reads every question, including the multi-part ones.
- 02
Tribble drafts it
It matches the question to your approved authorization summary and drafts the reply from your own documentation.
Sourcesystem security plan, boundary section. Owner: your security lead. - 03
Only what’s new gets reviewed
The proposal includes a module added after your last assessment, so this answer goes to your security lead with the boundary question marked. Answers that matched go straight through.
- 04
It goes back in their format
The answers go back into the agency’s file, ready for the proposal volume.
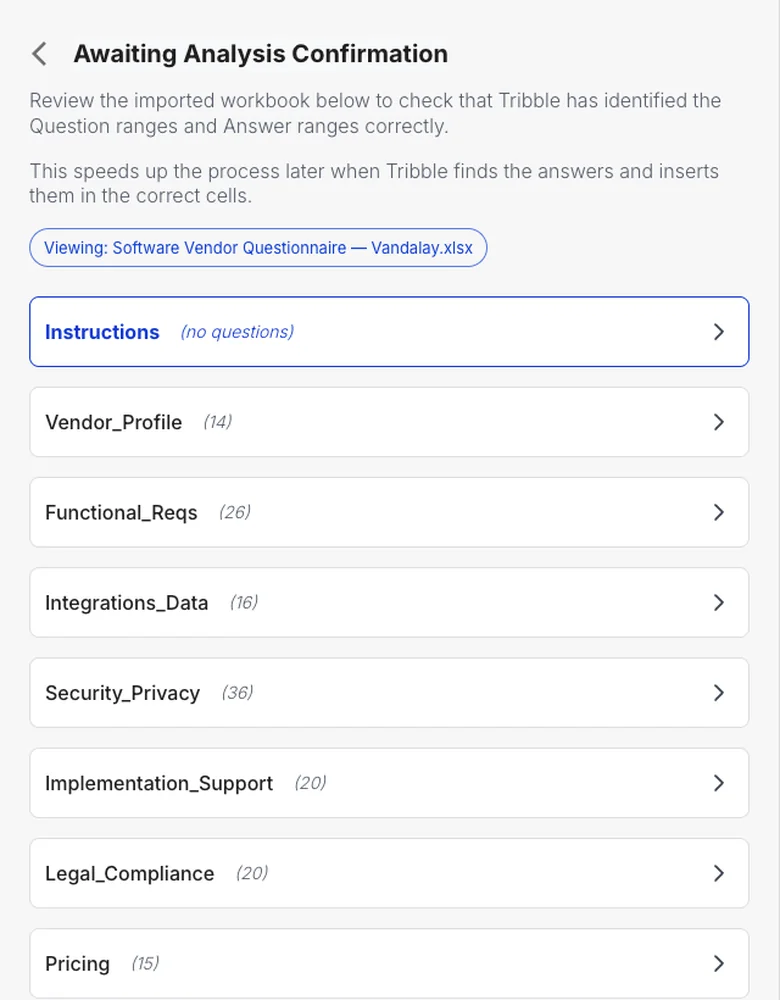
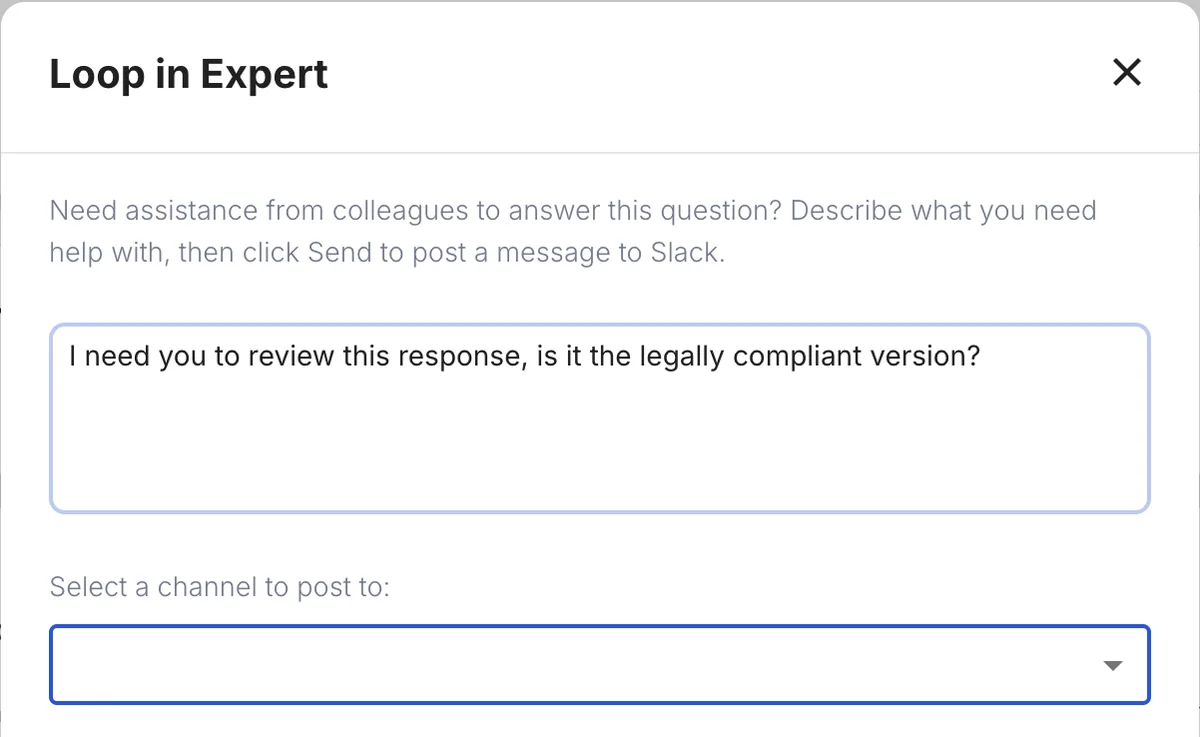
What it looks like in Tribble Respond.
Capture teams who know what the SSP actually says.
Tribble Engage answers capture managers and sales teams in Slack or Teams with the approved answer and its source, so nobody tells an agency the whole product is authorized when only part of it is.
Tribble Scribe records the call, drafts the follow-up and updates the CRM.
Example · Slack
@Tribble is the analytics module inside our FedRAMP boundary?
Not yet. The current authorization covers the core platform. Use the approved boundary statement, which lists the modules outside it.
Sourceauthorization boundary summary, approved by SecurityMapped to the frameworks agency reviewers use.
- FedRAMPAuthorization status, boundary and continuous monitoring
- NIST SP 800-53Security and privacy controls for federal systems
- NIST SP 800-171Protecting controlled unclassified information
- CMMCCybersecurity for the defense industrial base
- StateRAMPSecurity reviews for state and local government
- FAR and DFARSFederal and defense acquisition clauses
Tribble answers from your own evidence for each framework. Tribble itself is SOC 2 Type II compliant.
It learns from the tools your team already uses.
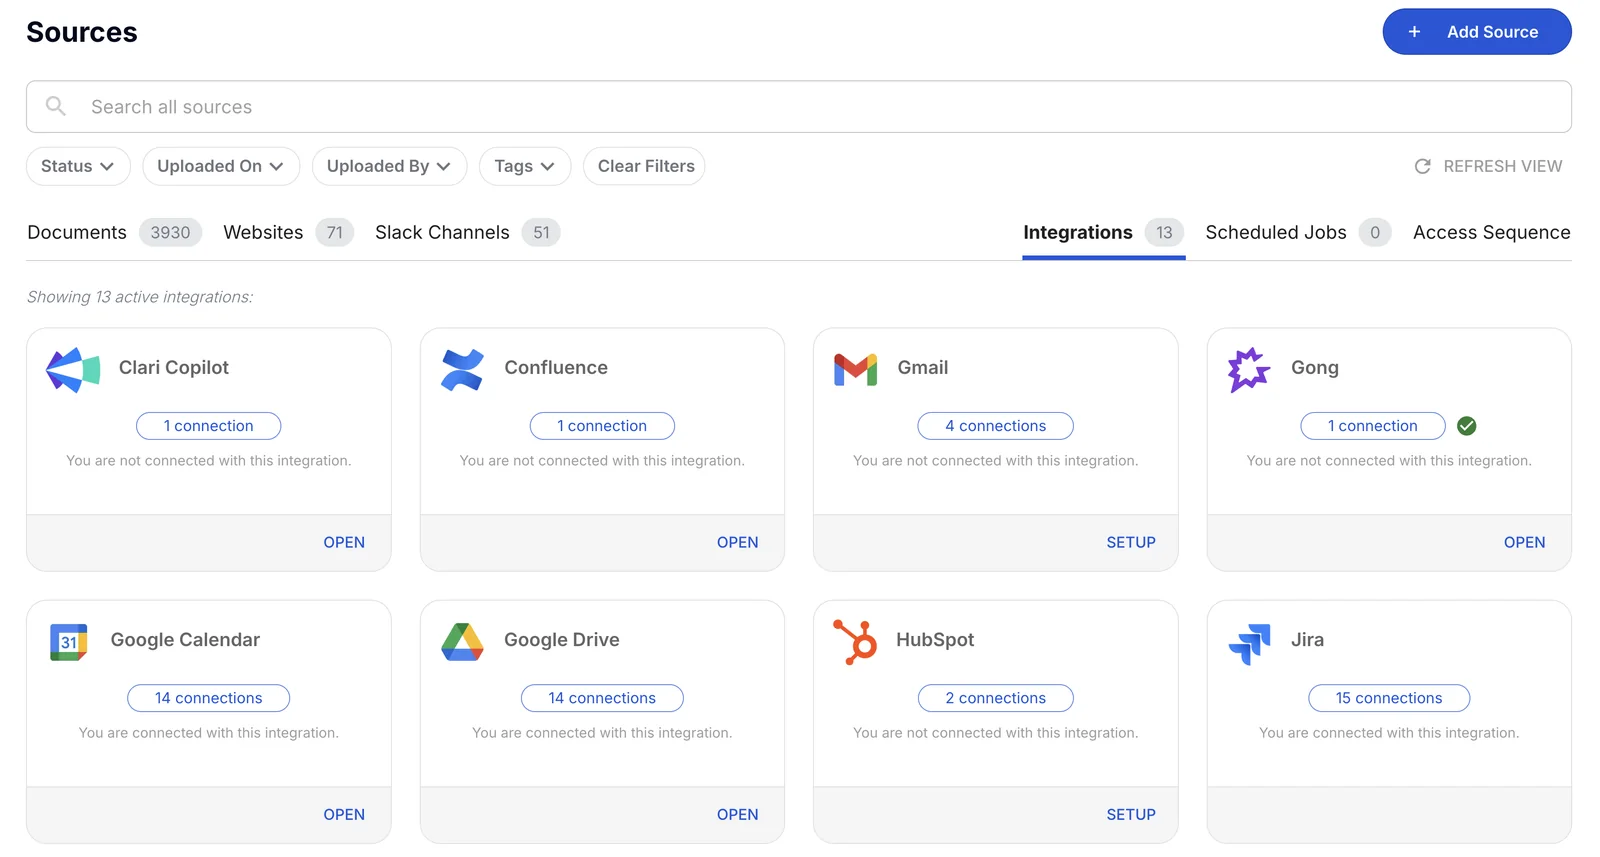
Your SSP and policies in SharePoint, past proposals in Google Drive, past performance write-ups in Confluence, capture notes in Salesforce. Tribble connects to them and keeps each one’s permissions.
Why general-purpose AI isn’t enough for government proposals.
| Compare | Generic AI | Tribble |
|---|---|---|
| Answers from | Public training data | Your approved proposals, SSP and past performance |
| Authorization claims | Can overstate what’s authorized | Only what your authorization actually covers |
| Control statements | Paraphrased from memory | From your current control implementation, with its source |
| Past performance | Invented or out of date | From the write-ups your capture team approved |
| When a control changes | Nothing updates | Update it once and the next proposal uses it |
| Audit trail | None | Who approved each answer, and when |
Proof from a team doing the same work.
Customer story · Revenue software
How Clari answered a 200-question RFP in under an hour
“What used to be a purely administrative process is now driving strategic insights that help us uncover product gaps and win more deals.”Brian Cody, VP, Sales Engineering, Clari Read the Clari story →
Clari doesn’t sell to government, but its governance, risk and compliance team does the same work: long security questionnaires, specialist review and a record of every answer.
Rated by the teams that use it.
Fall 2026, across RFP, AI Sales Assistant, AI Meeting Assistants, AI Proposal Generator Tools and Sales Analytics. Read the reviews on G2 →
FAQ
Common questions.
Can Tribble help with FedRAMP security questionnaires?
Yes. Tribble answers FedRAMP sections from your own system security plan, POA&M, control implementation statements and past assessment responses, and shows the source for each one. Tribble itself is SOC 2 Type II compliant.
How do we keep an authorization claim inside its boundary?
Answers are tied to the scope your security lead approved. When a question covers a component outside that boundary, Tribble doesn’t stretch the claim. It routes the question to your security lead.
Will the technical and management volumes say the same thing?
Every volume draws on the same approved answers, so a control or a staffing commitment reads the same way throughout. Anything new goes to its owner before it goes in.
Does Tribble handle state and local RFPs as well as federal?
Yes. Answers can be approved for one jurisdiction or for all of them, so a StateRAMP review and a federal RFP each get the answer that applies.
How is this different from our proposal library?
A library stores past volumes. Tribble knows which answers still match your current SSP and who approved them, and routes anything it can’t support to the right expert.
Bring the security volume that’s holding up a bid.
Send a redacted FedRAMP questionnaire or a recent RFP. We’ll answer it from your own documentation on the call, and show you which questions would go to security and contracts.
Book a working session